Last Updated: November 1, 2026
Quick Summary
To audit it asset disposal, test each retired asset from your register through approval, chain of custody, and sanitization to a verified data destruction certificate. Then reconcile the disposal manifest against your CMDB and asset register, and document every mismatch as a matched record, explained exception, or unexplained gap.
- Write down your audit scope, objectives, and starting asset inventory before testing anything.
- Whoever decommissions a drive should not be the person who certifies it was destroyed.
- Your asset register is the primary record; the vendor’s manifest is only supporting evidence.
- Risk-based sampling means auditing the highest-sensitivity data, largest volumes, and newest vendors first.
- Reconcile by serial number, not volume, and give every exception an owner and deadline.
Table of Contents
- What an IT Asset Disposal Audit Actually Proves
- Step 1: Define Disposal Policies, Approval Workflows, and Who Owns What
- Step 2: Test Asset Identification, Tracking, and Serial Number Records
- Step 3: Follow the IT Asset Disposal Chain of Custody From Pickup to Processing
- Step 4: Verify Data Sanitization and the Data Destruction Certificate for IT Assets
- Step 5: Put ITAD Vendor Due Diligence and Risk-Based Sampling to Work
- Step 6: Reconcile Disposal Records Against Your CMDB and Asset Register
- Step 7: Build Your IT Asset Disposal Audit Checklist and Handle Exceptions
- Frequently Asked Questions
What an IT Asset Disposal Audit Actually Proves
An IT asset disposal audit proves that every retired laptop, server, and drive left your control through an approved, documented path, and that the data on it is gone.
The core problem is that most teams treat an IT asset disposal audit as after-the-fact paperwork. The audit should test whether the process itself holds up.
Below are seven steps, from policy to exception handling, with the evidence to pull at each stage.
Audit Scope, Objectives, and the Asset Inventory You Start From
Before testing anything, write down what you are testing and why. Most failed audits skip this and chase the wrong records.
- Audit scope: which sites, asset classes, and date range are in play
- Audit objectives: what a pass looks like, in measurable terms
- Asset inventory: the starting list of every device that should be accounted for
Your inventory is the spine of the whole audit. Pull it from your asset register and CMDB, not from memory or a spreadsheet someone maintained by hand.
The NIST SP 800-88 guidelines for media sanitization define the sanitization categories auditors test against, so align your objectives with that language early.
Step 1: Define Disposal Policies, Approval Workflows, and Who Owns What
A disposal policy is only as strong as the approvals behind it. If anyone with a badge can walk a server out the door, no certificate will save the audit.
Map who can approve disposal, who physically releases the asset, and who signs off on data destruction.
A workable approval workflow looks like this:
- Asset owner requests decommission with business justification
- IT security confirms data sensitivity classification
- Finance confirms the asset is fully depreciated or written off
- Disposal is approved and logged with a ticket number
- Asset moves to a secure holding area with access controls
Document each approval with a timestamp and a name. During the audit, sample these records and check that no disposal happened without a matching approval.
Step 2: Test Asset Identification, Tracking, and Serial Number Records
Asset identification is where audits quietly fall apart. A device without a serial number is one you cannot prove you ever controlled.
Test your tracking by sampling assets from the register and tracing each one forward.
- Every retired asset has a recorded serial number
- Barcode or RFID scans create a timestamped trail
- Asset tags match the register, not just the box label
A common mistake is trusting the vendor’s manifest as the source of truth.
Assets that skip the scan step, like a drive pulled in a hurry and handed to a tech, become ghost assets.
Step 3: Follow the IT Asset Disposal Chain of Custody From Pickup to Processing
Chain of custody is the unbroken record of who held each asset, when, and where, from your loading dock to final destruction. A gap means the audit cannot confirm the asset was ever destroyed.
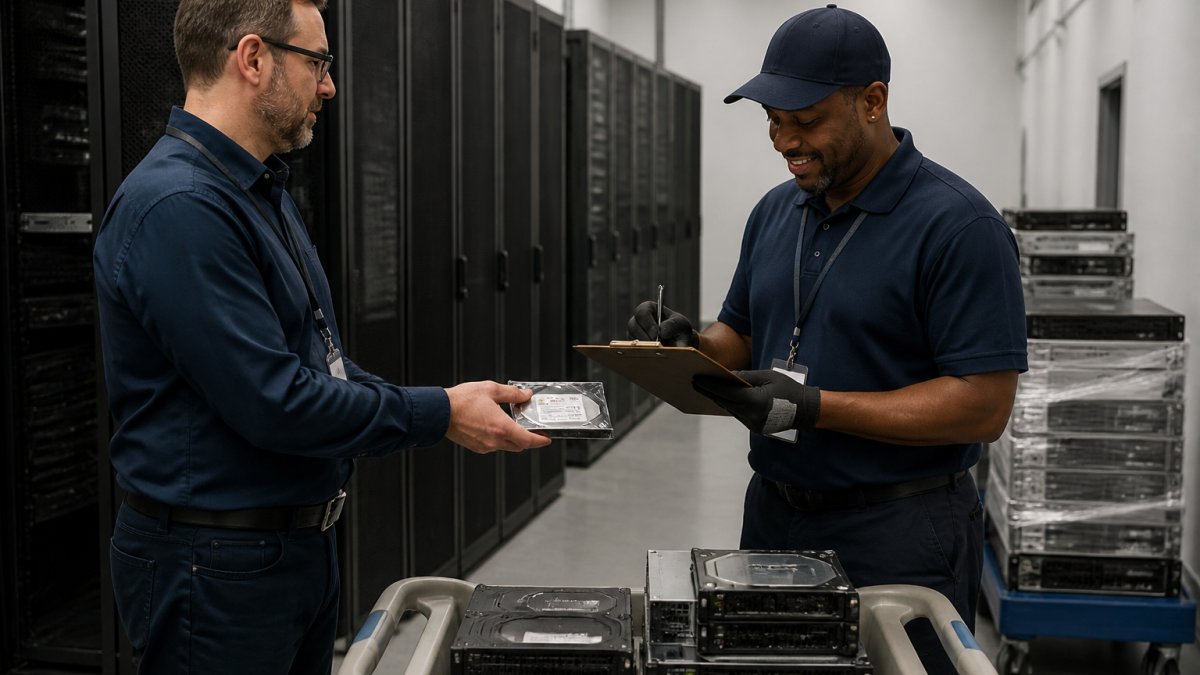
Walk the paper trail end to end:
- Collection request: who authorized pickup, and what was on the manifest
- Secure transportation: locked containers, sealed totes, driver sign-off
- Receiving: scan-in at the processing facility with date and time
Real-time tracking and digital logs beat paper. If your vendor hands you a signed form with no scan data behind it, ask how they reconcile the two. The record is the product shows what chain-of-custody records and documentation look like from the vendor side.
Step 4: Verify Data Sanitization and the Data Destruction Certificate for IT Assets
A data destruction certificate for IT assets is a signed record stating how, when, and by what method specific media were sanitized or destroyed.
Test the certificate against the standard it claims. If it says NIST 800-88, check whether the method matches the media type and the data classification.
For practical ways to validate what vendors hand you, our guide on how to verify data destruction certificates walks through the checks. If you need the standard itself in plain terms, NIST 800-88 hard drive shredding requirements explains what sanitization claims should rest on.
The EPA guidance on electronics and e-waste is worth reading alongside your environmental controls, since disposal records often serve both data and regulatory purposes.
Step 5: Put ITAD Vendor Due Diligence and Risk-Based Sampling to Work
ITAD vendor due diligence confirms a third-party vendor can do what its contract promises, before and during the relationship. Risk-based sampling tests that promise without auditing every serial number you ever retired. Establishing these verification protocols ensures that your internal security posture remains as robust as the standards maintained by Bay Safe and Lock when evaluating broader organizational vulnerabilities.
Vendor due diligence: what to request and verify
Build a due diligence file before the first pickup and refresh it annually. Request and independently verify:
- Business and insurance documents: current certificate of insurance, business license, and a signed master services agreement with data-breach notification terms.
- Certifications: confirm the vendor’s claimed certifications directly with the issuing body rather than accepting a PDF logo.
- Sanitization methodology: a written description of methods by media type (magnetic, flash, optical) and how they map to NIST SP 800-88 guidelines for media sanitization categories.
Record each item as verified, pending, or failed. A pending item is a finding, not a pass.
How to build a risk-based sample
Risk-based sampling means you do not audit every asset. You audit the ones that carry the most risk: the highest-sensitivity data, the largest volumes, the newest vendor, or the site with the weakest controls.
A practical method:
- Stratify the population. Split the disposal population by data classification, media type, site, vendor, and disposal date.
- Assign a risk score. Weight high-sensitivity data and unproven vendors highest; weight low-sensitivity, long-tenured vendor batches lowest.
- Select the sample. Draw a judgmental sample from the highest-risk strata and a small random sample from the rest so you can speak to the whole population.
- Size the sample to the control. For a high-risk stratum, test enough items to catch a single failure; for low-risk strata, a smaller random draw is defensible.
- Document the rationale. Write down why each stratum was weighted as it was. The sampling logic is itself auditable evidence.
| Sampling Trigger | Why It Gets Tested | Evidence to Pull |
|---|---|---|
| High-sensitivity data | Breach impact is highest | Sanitization cert, method, serial match |
| New vendor or site | Controls are unproven | Due diligence file, first pickup records |
| Large volume batch | Errors hide in scale | Manifest vs. scan log reconciliation |
| Prior exception | Repeat failure risk | Remediation record, re-test result |
| Media type change | Method may not fit media | Method-to-media mapping, test result |
Control testing procedures
For each sampled asset, run the same sequence so results are comparable:
- Existence: confirm the serial number appears in the asset register and CMDB.
- Authorization: match the disposal to an approved ticket with a named approver and timestamp.
- Custody: trace the chain-of-custody record from pickup scan to receiving scan to processing event.
Record each test as pass, fail, or not tested, with the evidence reference. A “not tested” result is a scope limitation you must disclose, not a silent omission.
Test the certificate against the standard it claims. If it says NIST 800-88, check whether the method matches the media type and the data classification. A cleared drive and a shredded drive are not the same claim.
For practical ways to validate what vendors hand you, our guide on how to verify data destruction certificates walks through the checks. If you need the standard itself in plain terms, NIST 800-88 hard drive shredding requirements explains what sanitization claims should rest on.
The EPA guidance on electronics and e-waste is worth reading alongside your environmental controls, since disposal records often serve both data and regulatory purposes.
Step 6: Reconcile Disposal Records Against Your CMDB and Asset Register
Reconciliation is the moment of truth: compare three sources and explain every difference. The hard part is what to do when serials do not match, when the same asset appears twice, or when finance wrote off an asset that never shows a disposal record.
Line up your CMDB, your asset register, and the vendor’s disposal records. Then account for every asset as one of three outcomes: matched, explained exception, or unexplained gap. Unexplained gaps are audit findings, full stop.
The reconciliation procedure
- Export the disposal manifest with serial numbers, media type, and processing date.
- Normalize the data. Strip whitespace, standardize case, and resolve known serial-format variants before matching. A formatting mismatch is not a missing asset.
- Match each serial against the register and CMDB using an exact match first, then a fuzzy match for known variants.
- Flag assets in the register with no disposal record, potential ghost assets still in service or lost.
- Flag disposal records with no matching asset, potential unauthorized disposals or vendor errors.
- Flag duplicates where one serial appears in more than one disposal record or register entry.
- Tie to finance. Compare the disposal list against fixed-asset write-offs and depreciation schedules to catch assets retired on paper but never physically disposed of, or vice versa.
- Investigate every mismatch before closing the audit, and record the disposition of each.
A common mistake is reconciling to the vendor’s count instead of your own. Volume matching proves nothing. Serial matching proves everything.
Handling duplicates, write-offs, and depreciation
- Duplicate records: determine which record is authoritative. If the same serial was disposed twice, one record is false and must be corrected at the source.
- Written-off but not disposed: finance removed the asset from the books but no disposal record exists. Treat it as a ghost asset until located or documented as lost.
- Disposed but not written off: the asset left the register but remains on the books. Route it to finance for correction.
Exception handling and escalation
Every exception needs an owner, a deadline, and a disposition. Use a simple exception log:
| Exception Type | Owner | Escalation Path |
|---|---|---|
| Missing certificate | Vendor manager | Security and compliance |
| Broken custody record | Logistics lead | Vendor manager and compliance |
| Failed sanitization | IT security | Compliance and legal |
| Unapproved disposal | Asset owner | Compliance and HR |
| Unexplained gap | Audit lead | Compliance and security |
Escalate unexplained gaps to compliance and security, and do not close the audit until each has a resolution or an accepted risk note signed by the appropriate owner. A repeat exception from the same vendor or site should trigger a re-test of that stratum next cycle.
An accepted risk note is not a pass. It is a documented decision to proceed despite a known gap, and it should name the decision-maker and the review date.
Step 7: Build Your IT Asset Disposal Audit Checklist and Handle Exceptions
Your IT asset disposal audit checklist turns the previous six steps into a repeatable, testable document. Build it once, then run it every cycle. ITAD shows the service scope and documentation you should be auditing against.
- Disposal policy approved and current
- Approval workflow logged with names and dates
- Serial numbers recorded for every retired asset
Frequently Asked Questions
How do you verify that data was securely destroyed before equipment disposal?
Ask for the sanitization record tied to each serial number, not a blanket statement. A valid record names the method used, such as physical shredding or a NIST 800-88 compliant erasure, the date, the technician, and the device identifier. Then confirm the certificate of destruction matches your own asset register line by line. If any serial number is missing or the method is described vaguely, treat that device as unverified and escalate it before the record is closed.
What records should a company keep for disposed IT assets?
Keep the disposal policy and approval sign-offs, the asset register extract for each retired device, collection and transport documents, the chain of custody form, sanitization and destruction certificates, and any recycling or diversion reporting. Store them together by batch so an auditor can trace one device end to end without hunting across systems. Retention periods vary by regulation and contract, so set one in policy and apply it consistently rather than letting each department decide.
How do you audit an IT asset disposition vendor?
Start with ITAD vendor due diligence before the contract: certifications, downstream partners, insurance, and written data handling procedures. Once work begins, test the vendor with unannounced spot checks, compare returned certificates against your records, and ask for documentation on how devices that fail sanitization are handled. Segregation of duties matters here too, so the person who approves a pickup should not be the only person reviewing the vendor’s paperwork.
What are common IT asset disposal compliance gaps?
The recurring gaps are devices retired without a matching disposal record, certificates that list batch totals instead of serial numbers, chain of custody forms missing a signature or timestamp, and recycling claims with no supporting weight or diversion data. Another frequent one is approval workflow bypass, where a technician drops hardware at a recycler without a collection request. Risk-based sampling catches most of these quickly because the exceptions cluster around a few batches and a few people.
Auditing IT asset disposal is hard because the proof lives in many places: policies, scans, manifests, and certificates that must all agree. Erecycler has spent 27 years building that proof into the process itself, with documented chain of custody for all assets, hard drive shredding to NIST 800-88 standards, and sustainability metrics and diversion reporting your compliance officer can actually use. Get started with Erecycler and turn your next disposal audit into a clean, defensible record.
